
Customer Authentication
Unified, secure authentication across customer-facing surfaces
Customer authentication overview
Tiquo uses the same secure customer authentication system across its customer-facing tools.
- Passwordless OTP: email-based one-time passcodes
- Customer Portal: self-service access
- DOM Package: headless browser authentication and authenticated customer-flow embeds
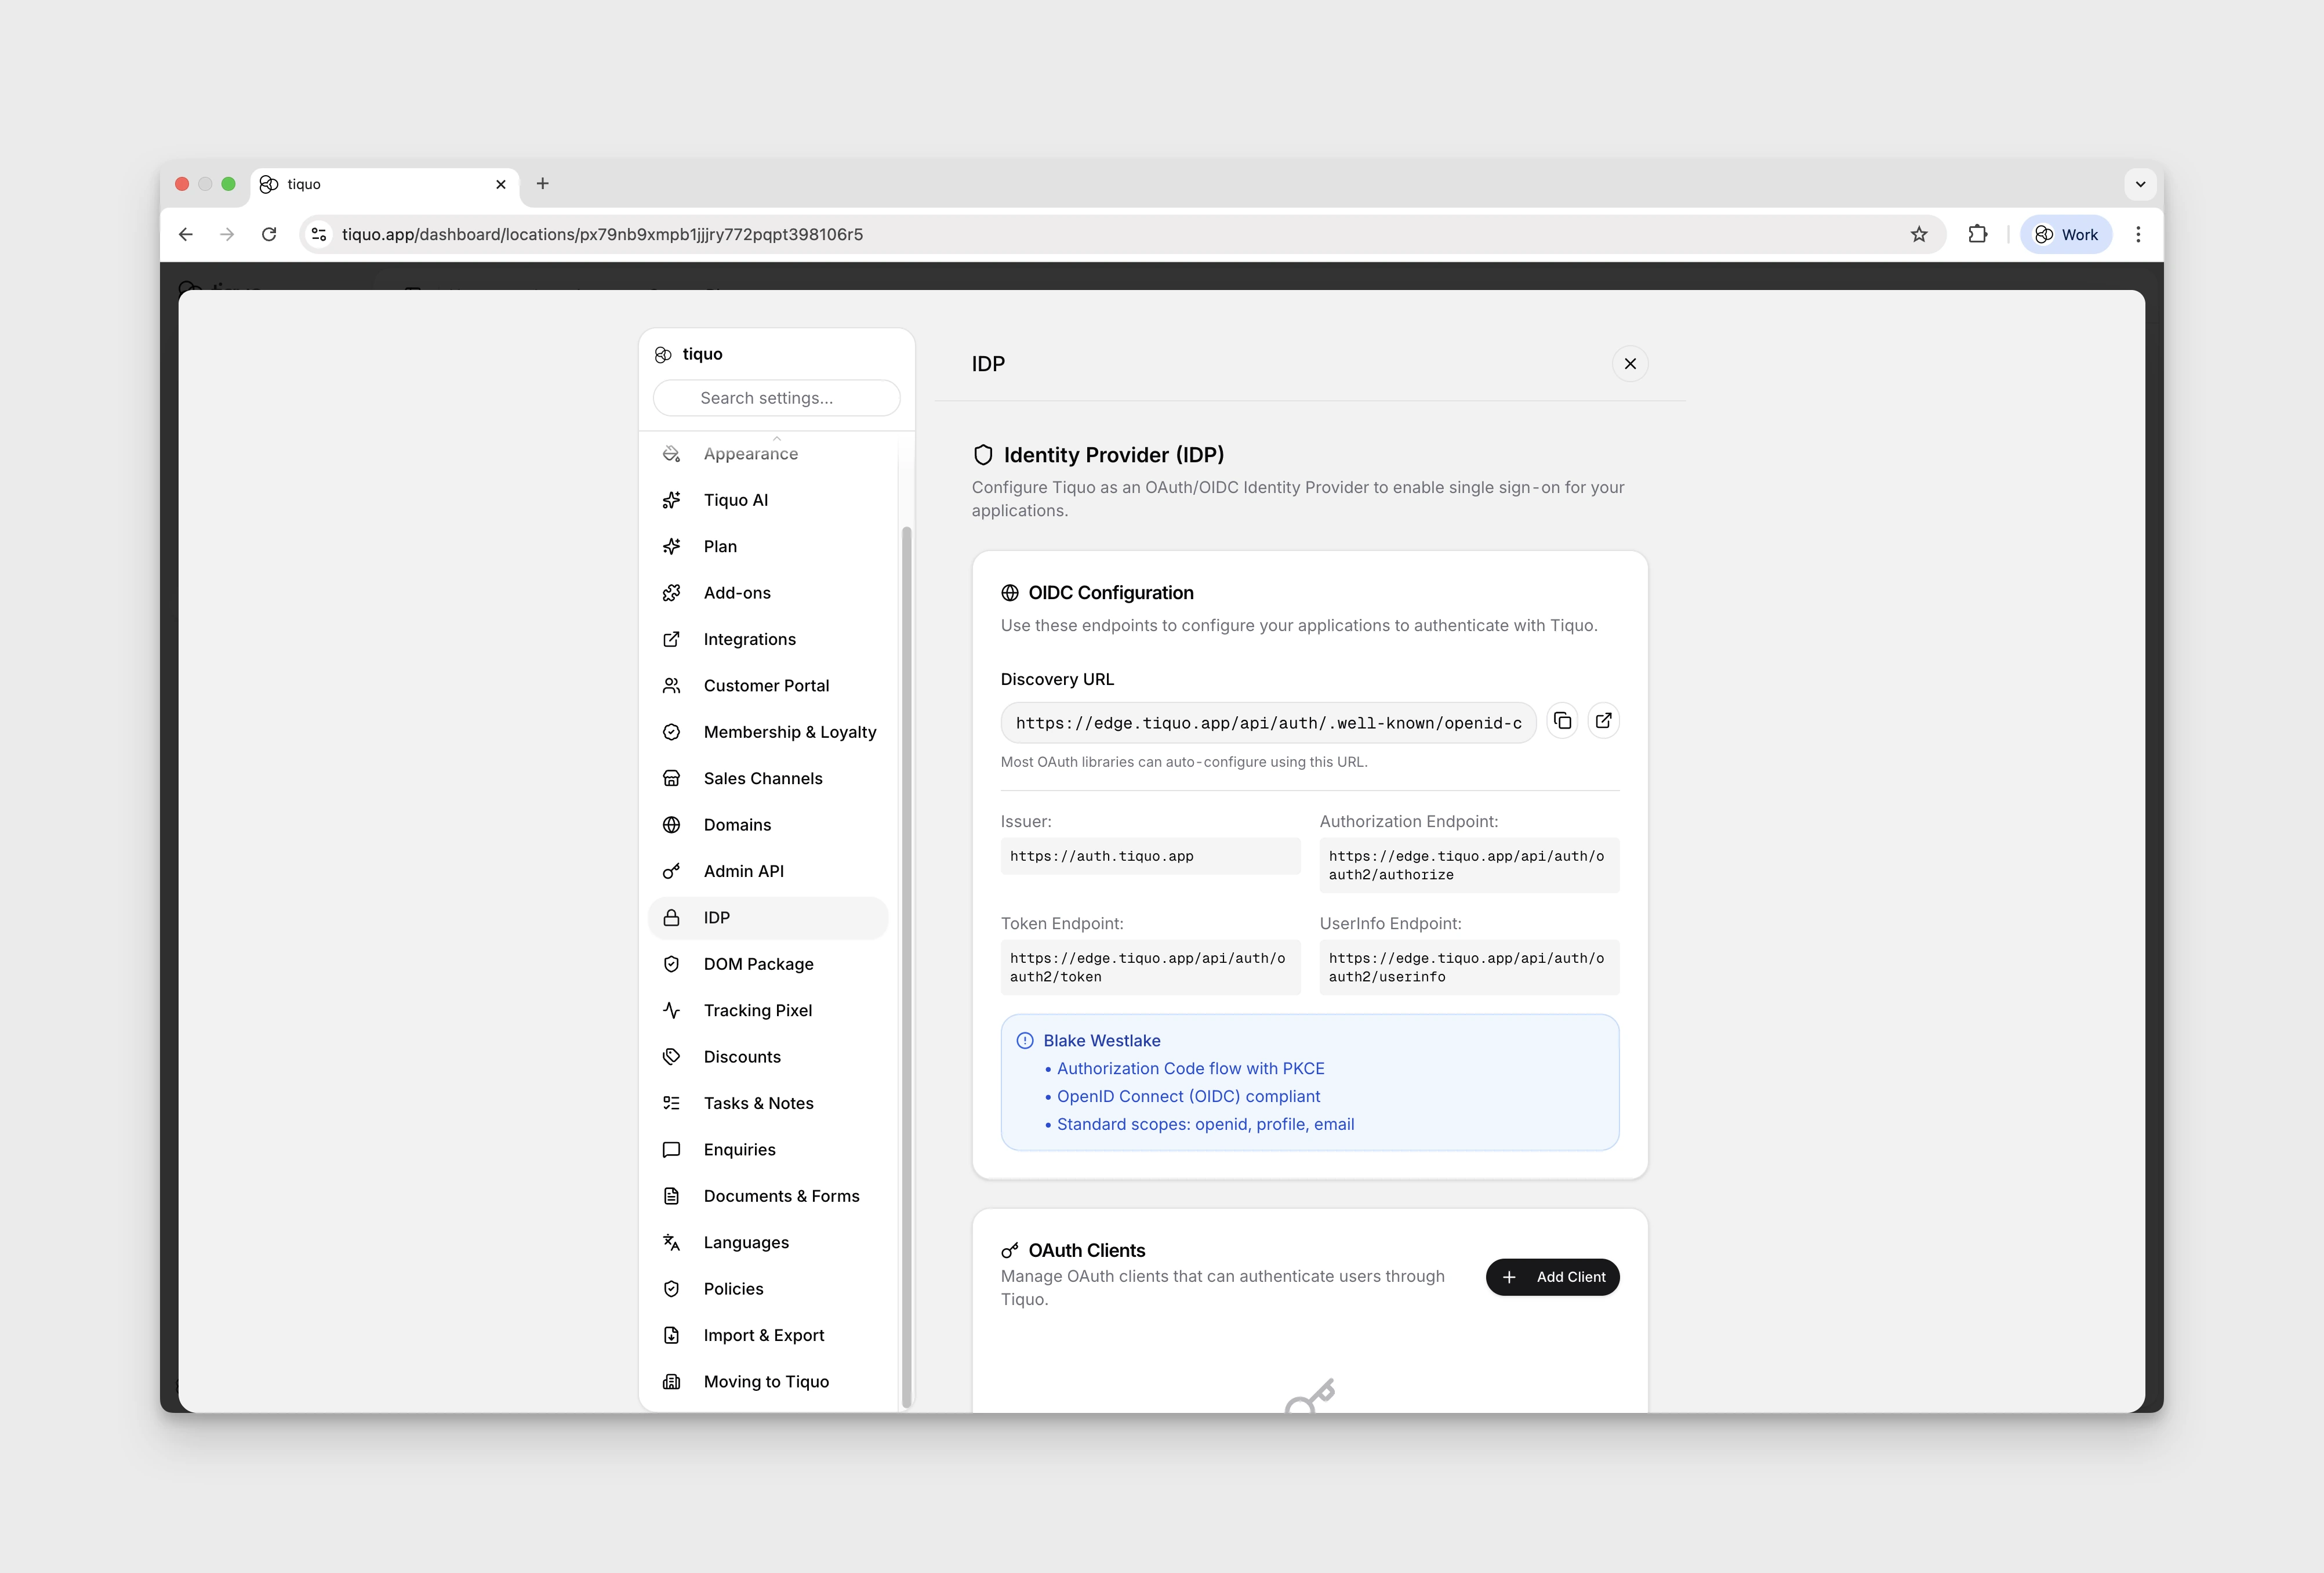
- OIDC / OAuth IDP: identity provider capabilities
This approach removes the need for passwords, reduces friction, and improves security while providing a consistent identity across all customer touchpoints.
Customer sessions
When a customer authenticates, Tiquo creates a secure session using industry-standard tokens.
| Token Type | Purpose |
|---|---|
| Access Tokens | Used to authenticate requests to the Customer API |
| Refresh Tokens | Used to obtain new access tokens without reauthentication |
| ID Tokens | Issued when using the OIDC / OAuth IDP |
All unexpired access tokens can be used to authenticate Customer API requests, allowing secure interaction with bookings, orders, customer data, and other customer-scoped resources.
Session handling is consistent across:
- Customer Portal
- Websites and applications using the DOM Package
- Customer Flows
- Third-party systems using OIDC/OAuth
Consent & security
Customer consent is a core part of Tiquo's authentication and tracking model.
Once a customer has provided consent:
- Their device can be recognised even when they are not actively logged in
- Activity can be associated with their customer profile across sessions
- Interactions can be tracked consistently across websites, apps, Customer Portal, Customer Flows, and embedded experiences
This allows Tiquo to:
- Maintain continuity of customer journeys
- Improve analytics and attribution
- Power personalisation and predictive models
Customers can withdraw consent at any time, after which:
- Device-level identification is disabled
- Cross-session tracking is disabled
- Privacy is fully respected
All consent handling respects applicable privacy regulations.